Presents
Bharat RegTech Summit 2026
Governance, Risk and Compliance for BFSI, Reimagined.
When
13th Oct 2026
Where
Mumbai
What to expect
600+
Footfall
30+
Speakers
20+
Live sessions
3+
Masterclasses
2
Product & Report launches
5
Demos
Join Us As
Speaker
Bring a practitioner's view on governance, risk, compliance or cyber resilience.
Sponsor
Put your brand in front of India's BFSI GRC and cybersecurity decision-makers.
Exhibitor
Showcase GRC, cyber and compliance tooling to a 100% BFSI audience.
Ecosystem Partner
Chapters, associations and communities, co-build the agenda and outreach with us.
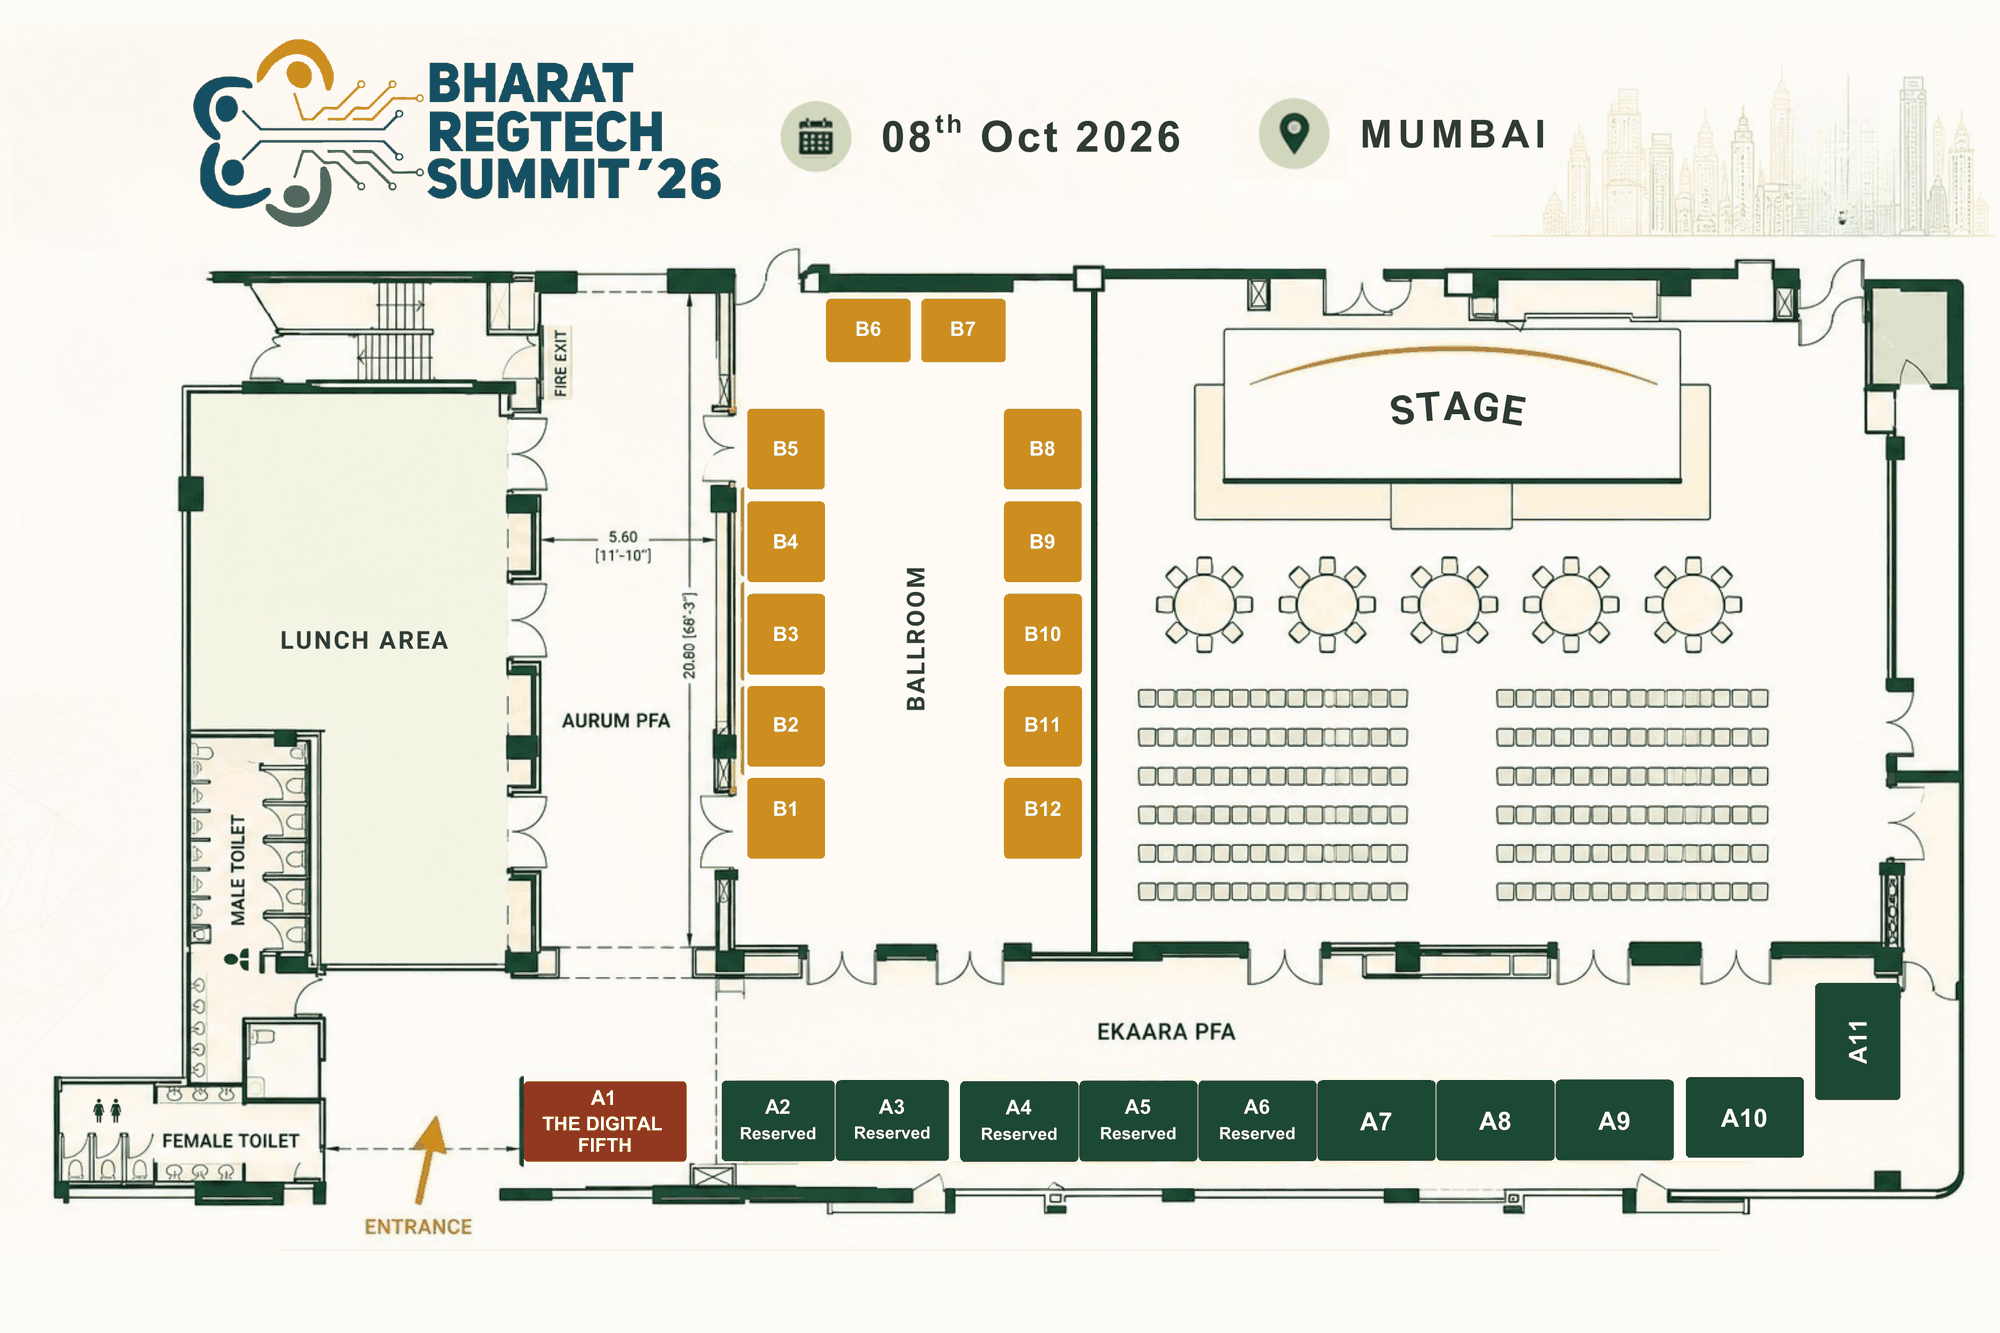
Exhibitors 2026
About the organiser
The Digital Fifth, Asia's leading consulting firm on digital finance.
The Digital Fifth is the organiser of Bharat Fintech Summit and India InsurTech Summit.
Our advisory work sits inside banks, NBFCs, fintechs and insurers as they build out governance, risk and compliance functions: the practitioner's view we bring to this stage. This isn't a summit designed by an events company; it's designed by the same consultants who sit across the table from CISOs and compliance heads every week.
Why this event
By Practitioners, For Practitioners.
Regulators across banking, markets, insurance and data privacy are rewriting BFSI's compliance stack at a pace this industry hasn't seen before, because the cost of falling behind isn't a penalty, it's customer trust. Knowing a guideline exists is step one; the real work is understanding why it exists, what it protects, and how leading teams stay ahead of it instead of scrambling to catch up. This summit brings the industry's best practitioners together to walk through the emerging regulations, their significance, and, above all, the implementation playbook.
01
Built by consultants, not event planners
Every session is shaped by advisors who sit across the table from risk, compliance and technology leaders every week; the agenda comes from live client work, not a generic GRC template.
02
Tracks the regulation as it's issued
This edition's sessions cover the RBI's new Cybersecurity, Technology & Resilience Framework and its draft Data Governance guidance: the two directions currently reshaping how boards and CISOs plan the year ahead.
03
One framework across regulators
Regulators across banking, markets, insurance, identity and data privacy are read together against a single control map, so you leave with one playbook instead of five disconnected checklists.
04
100% BFSI, no dilution
Every delegate maps back to a bank, NBFC, fintech or insurer mandate, not a generic IT security crowd, no vendor-only audience.
05
Implementation-first, not just interpretation
Sessions are built around the “how”, not the “what”: masterclasses and live demos walk through the actual playbook, not just what a clause says.
06
Data governance, given its own room
As RBI's draft guidance turns data into a board-level asset, sessions dig into data ownership, stewardship and lifecycle controls end-to-end, not just DPDPA consent boxes.
The Landscape
A decade of GRC, risk, compliance and data governance in India.
Data Privacy
2011
SPDI Rules
Cybersecurity
2016
RBI Cybersecurity Framework
Governance
2023
IT GRC
Governance
2023
IT Outsourcing
Data Privacy
2023
DPDPA Enacted
Compliance
2025
Digital Lending Guidelines
Data Privacy
Nov '25
DPDP Rules Notified
Data Governance
Jul '26
Draft Data Governance Guidance
Cybersecurity
Jul '26
Cybersecurity & Resilience Framework
Deadline
May '27
DPDP Rules Compliance Deadline
The backdrop this summit is built against, spanning data privacy, cybersecurity, governance and data-governance regulation.
Three themes
The agenda, built around what practitioners actually own.
Three standing themes that structure the day's sessions, masterclasses and launches, each one owned by a different function inside a regulated entity.
01
GRC
Governance, risk and compliance read as one connected discipline: board accountability, enterprise risk and regulatory obligations mapped to a single control framework.
02
Data Governance & DPDPA
RBI's draft Data Governance guidance and the DPDPA read together: data ownership, stewardship, consent and lifecycle controls, and what “compliant by design” actually looks like.
03
Cybersecurity
Building resilience against the threats regulators are now writing directions about: RBI's new Cybersecurity, Technology & Resilience Framework, SOC design, and cloud security.
Who will attend
A boardroom conversation, not a consultants' meetup.
Built for the people who own the decision, not the people who advise on it: CEOs and board members alongside the CXOs who report to them.
600+
Expected delegates
100% BFSI focused
The full BFSI ecosystem in one room.
Banks
PSU, private, foreign, Small Finance Banks and Urban Co-operative Banks.
NBFCs
Asset finance and digital lending platforms.
Fintechs
Payments, lending and wealth-tech.
Security Providers
Cybersecurity vendors and SOC/VAPT service providers serving regulated entities.
Insurers
Insurers and digital insurance platforms navigating IRDAI's cyber and governance guidelines.
RegTechs
Compliance, GRC and cybersecurity tooling providers building for BFSI.
From the Blog
What the team is reading the regulation to mean, between editions.